by Gloria Bakerian | Aug 20, 2026 | Cybersecurity
TL;DR Help desk security requires more than trusting a caller who knows an employee’s name, title, or personal information. Before resetting a password, replacing an MFA method, or granting account access, support staff need a consistent way to verify that the...
by Gloria Bakerian | Aug 18, 2026 | Cybersecurity
TL;DR Cybersecurity incident reporting means promptly telling the appropriate person when something looks suspicious, even when you are unsure whether it is a real threat. Reporting a questionable email, lost device, unfamiliar visitor, or accidental click gives...
by Gloria Bakerian | Aug 14, 2026 | Cybersecurity
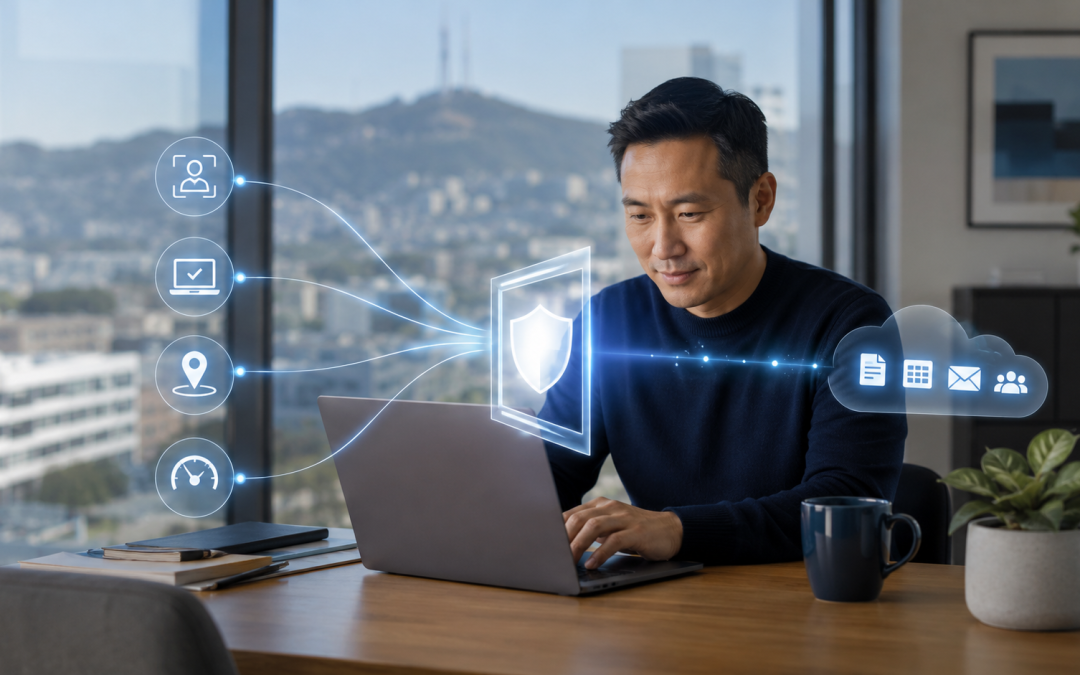
TL;DR Conditional access gives a business rules for deciding who can reach Microsoft 365, from which devices and locations, and under what security requirements. It can require MFA, block legacy sign-ins, restrict unmanaged devices, or stop suspicious access. The...
by Gloria Bakerian | Aug 14, 2026 | Cybersecurity, Uncategorized
TL;DR: The Suisun City cyberattack disrupted 911 routing, dispatch, records, and city operations, but essential response continued through alternate systems and regional support. Bay Area businesses should take the same lesson seriously: prevention matters, but tested...
by Gloria Bakerian | Aug 12, 2026 | Cybersecurity
TL;DR Social engineering attacks manipulate people rather than directly attacking technology. Criminals impersonate trusted individuals, create urgency, and exploit normal business habits to steal passwords, money, or sensitive information. Businesses can reduce the...
by Gloria Bakerian | Aug 11, 2026 | Cybersecurity
TL;DR Microsoft AI security applies Zero Trust principles to AI agents that can access data and take action. Before deployment, give each agent a defined purpose, narrow permissions, reliable logging, an accountable owner, human approval for high-impact actions, and a...